 Security
 audit
A full review of your WordPress install with a written report, ranked by real risk.
- Core, plugin and theme versions against known CVEs
- User roles, admin accounts and login exposure
- Server, PHP and file-permission review
WordPress security consultancy
We've been building it since 2007. Now we help you keep it secure.
Security audits, hardening and hacked-site recovery from the team behind Gabfire Themes. We find what's exposed, fix it, and watch new plugin vulnerabilities for you.
What we do
Some clients want a second opinion. Others want us to log in and handle it. We do both, and we tell you plainly what's urgent and what can wait.
A full review of your WordPress install with a written report, ranked by real risk.
We apply the fixes from the audit, or from your own scanner, on staging first.
Redirects, spam pages, a host suspension or a Google warning. We clean it, close the hole that let them in, and help with blacklist removal.
Get help nowWe track new disclosures against your exact plugin list and act when one affects you.
An hour with a specialist to talk through an incident, a plugin choice, a hosting move or a compliance question.
Plugin and theme authors: we review nonces, capability checks, escaping and SQL before your next release.
Free resource
Every WordPress core, plugin and theme vulnerability published to the CVE list in 2026. Search by plugin, CVE ID or weakness type.
Free stack check
Paste your plugin and theme names or wordpress.org slugs, one per line. We match them against this year's disclosures. Nothing leaves your browser.
A match means a vulnerability was published for that plugin. Compare the affected versions with what you have installed, or let us do it.
Example list loaded. Replace it with yours.
How an engagement runs
Your URL, host, and plugin list. If you've been hacked, what you're seeing.
Read-only review first. You get a report with every finding ranked by risk.
Patching and hardening on staging, then production, with backups at every step.
Optional monitoring matches new disclosures against your stack.
Gabfire Themes
The theme shop that started it all is open. Newspaper, magazine, business and niche themes, with the support our members have relied on since 2008.
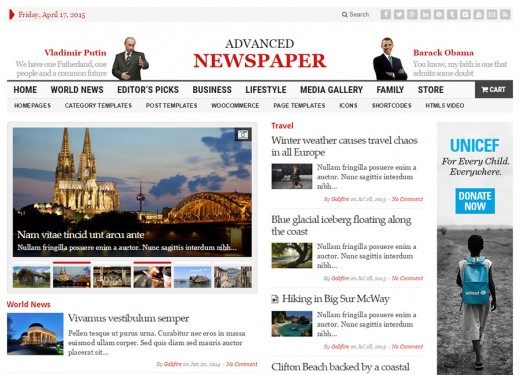
Newspaper
Our best seller. Launch a full online newspaper with sections and ad slots in minutes.
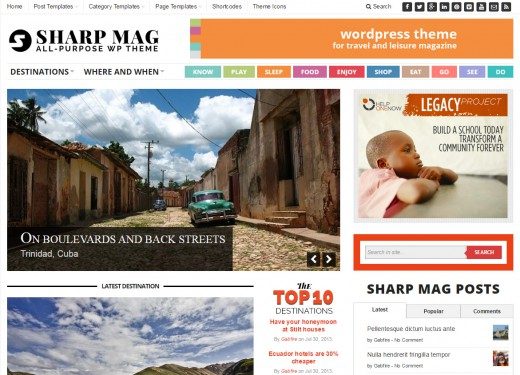
Magazine
A clean magazine layout with generous white space that lets photos and long reads stand out.
Business
An elegant one-page theme for businesses and portfolios. 22,000 lines of careful code.
Events
A responsive multipurpose theme for conferences, festivals and any event that needs a home online.

Travel
A sleek blog and magazine theme that also suits travel agencies showcasing destinations.
Over 40 themes built for clients, and Gabfire's support was the best tech support of any of them.
Jean Pierre, Founder & Publisher, Scottsdale Lifestyles Magazine (paraphrased)From the blog
WordPress fixes, snippets and hosting lessons from our own client work. Read the blog
Looking for an easy way to display captions for featured images on your WordPress website? The get_the_post_thumbnail_caption() function can help you do…
24 Mar 2023 · WooCommerceIf you're an e-commerce store owner or a developer working with WooCommerce, you might have come across the WC_Price function. This function…
28 Sep 2021 · HostingAfter Apache got updated on our Ubuntu distro, we suddenly started have Error 500 of Plesk shown on all our sites. Then…